Add privacy to the services you offer your clients
Your clients already rely on you for their systems and security. Sooner or later one asks: “We had a breach, do we have to report it?” Or, “Our customer or insurer wants to know what we have in place.”
ClearBreach lets you answer both, and review their new vendors, for every client from one account, each in their own name. You offer a service you could not before, without building the assessments, researching the law or writing the documents yourself.
From $1,645 a year for 5 clients, plus applicable taxes: $329 a client or less, where the same plan bought directly is $799. Covers your clients under PIPEDA, Alberta PIPA and BC PIPA; Quebec Law 25 is outside our scope.
Your clients will need help at different moments
Privacy work does not only come up when something goes wrong. Here is what you can do in each case.
A client has a privacy incident
Run the breach assessment with them: whether they must report, to whom and by when, under each law that applies, with the reports and letters written.
A client’s customer sends a questionnaire
Run the compliance assessment: what they have in place, what is missing, and the policies and procedures to show for it.
A client’s insurer asks what they have in place
The same compliance assessment gives them a dated record of their privacy practices to answer from.
A client is adding a new vendor or software
Run a privacy impact assessment before they sign: which law covers it, what to do first, and a completed PIA. Unlimited on every MSP plan.
A client wants the basics in place
Start with the compliance assessment and work through what to fix first, with the documents written from their answers.
Three ways to help your clients, one account
Your clients receive the assessments and documents under their own name. You run the work from your provider account.
| Assessment | When the client needs it | What the client receives |
|---|---|---|
| Breach assessment | An incident involving personal information | An answer under each law that applies, what to do and by when, and the regulator reports and notice letter written |
| Compliance assessment | A customer, an insurer, or getting the basics in place | Where they stand, every gap with what closes it, and their privacy policies and procedures written from their answers |
| Privacy impact assessment | A new vendor, system or project | Which law covers each flow of information, the duties to meet first, and a completed PIA to keep or file |
Each client receives: the Business plan, with 3 breach assessments a year and an annual compliance assessment; unlimited privacy impact assessments; and their own portal and records.
One provider account, separate client records
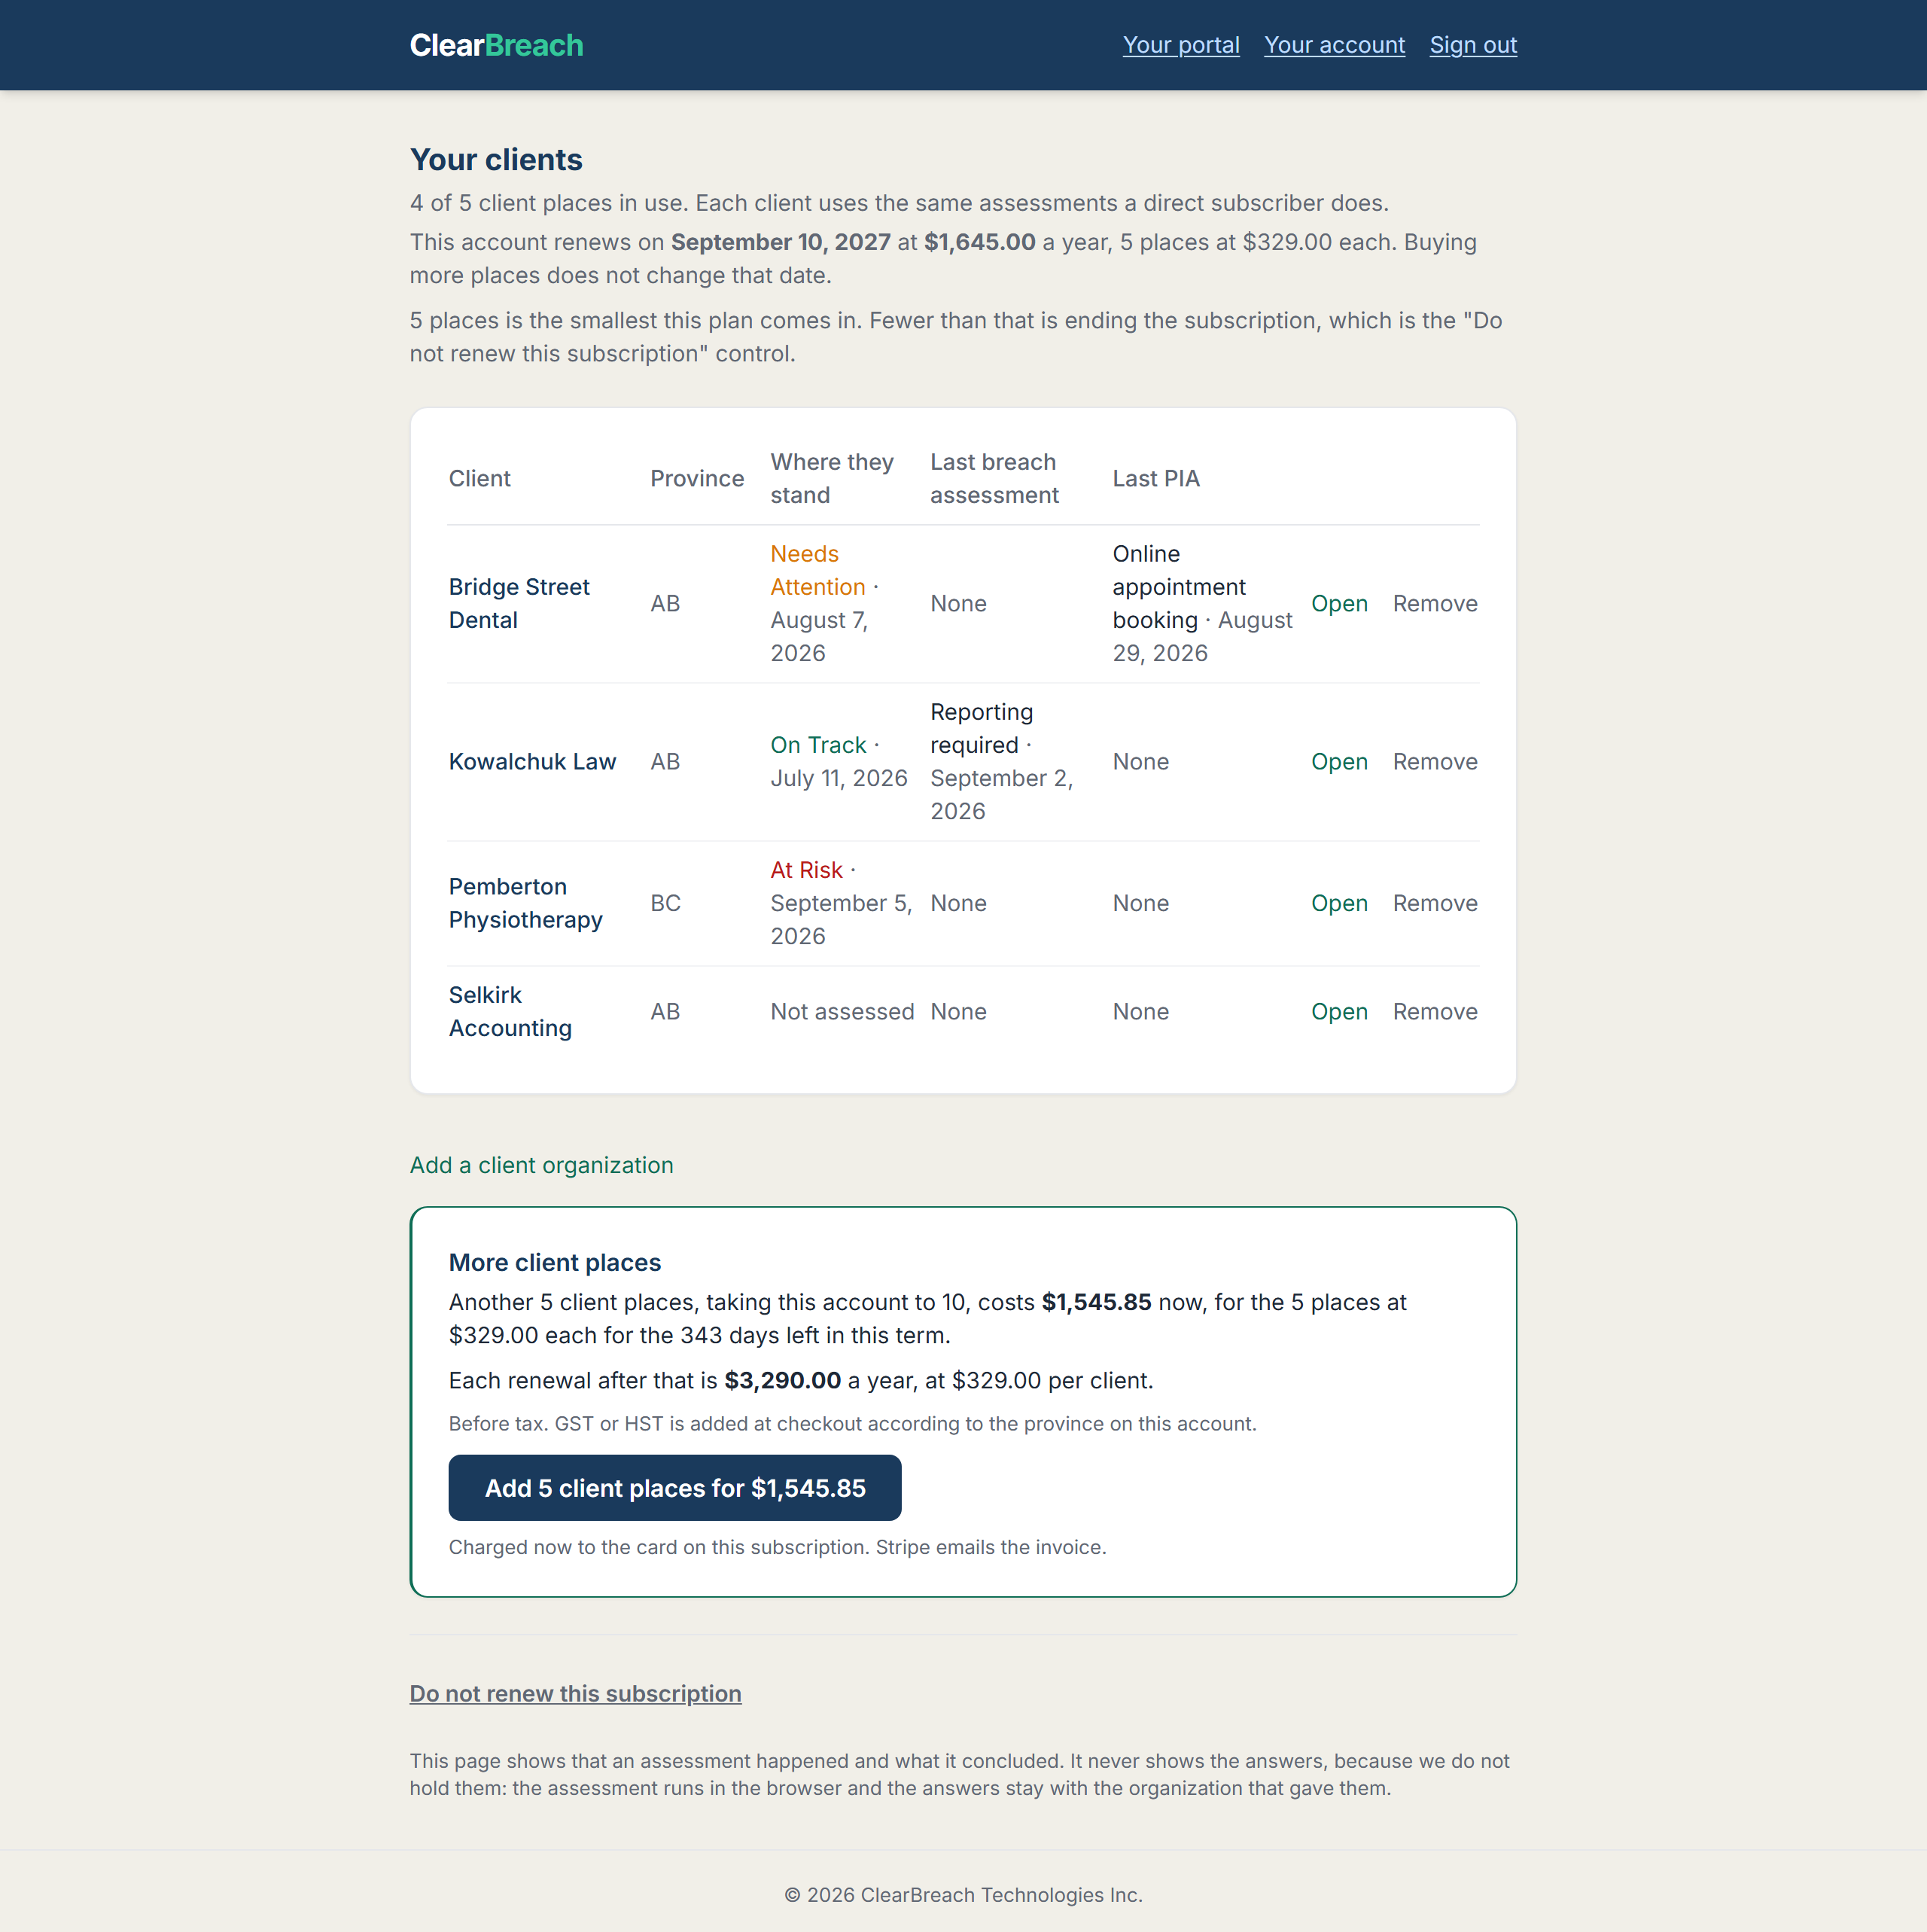
Pick a client, run the assessment, and the result stays with that client.
Every client on one screen
Your clients are listed with the province each operates in and where their compliance assessment stands. You do not sign in and out of anything.
Each assessment in the client’s name
Open a client and run a breach, compliance or privacy impact assessment for them. Every assessment is recorded under that client, not under you.
Who did what, when a client asks
While you work for a client, a banner says which one, and the record keeps the name of the person who ran it. The two never get mixed up.
One client never uses up another
Each client has its own assessment allowance. Running an assessment for one client takes nothing from another.

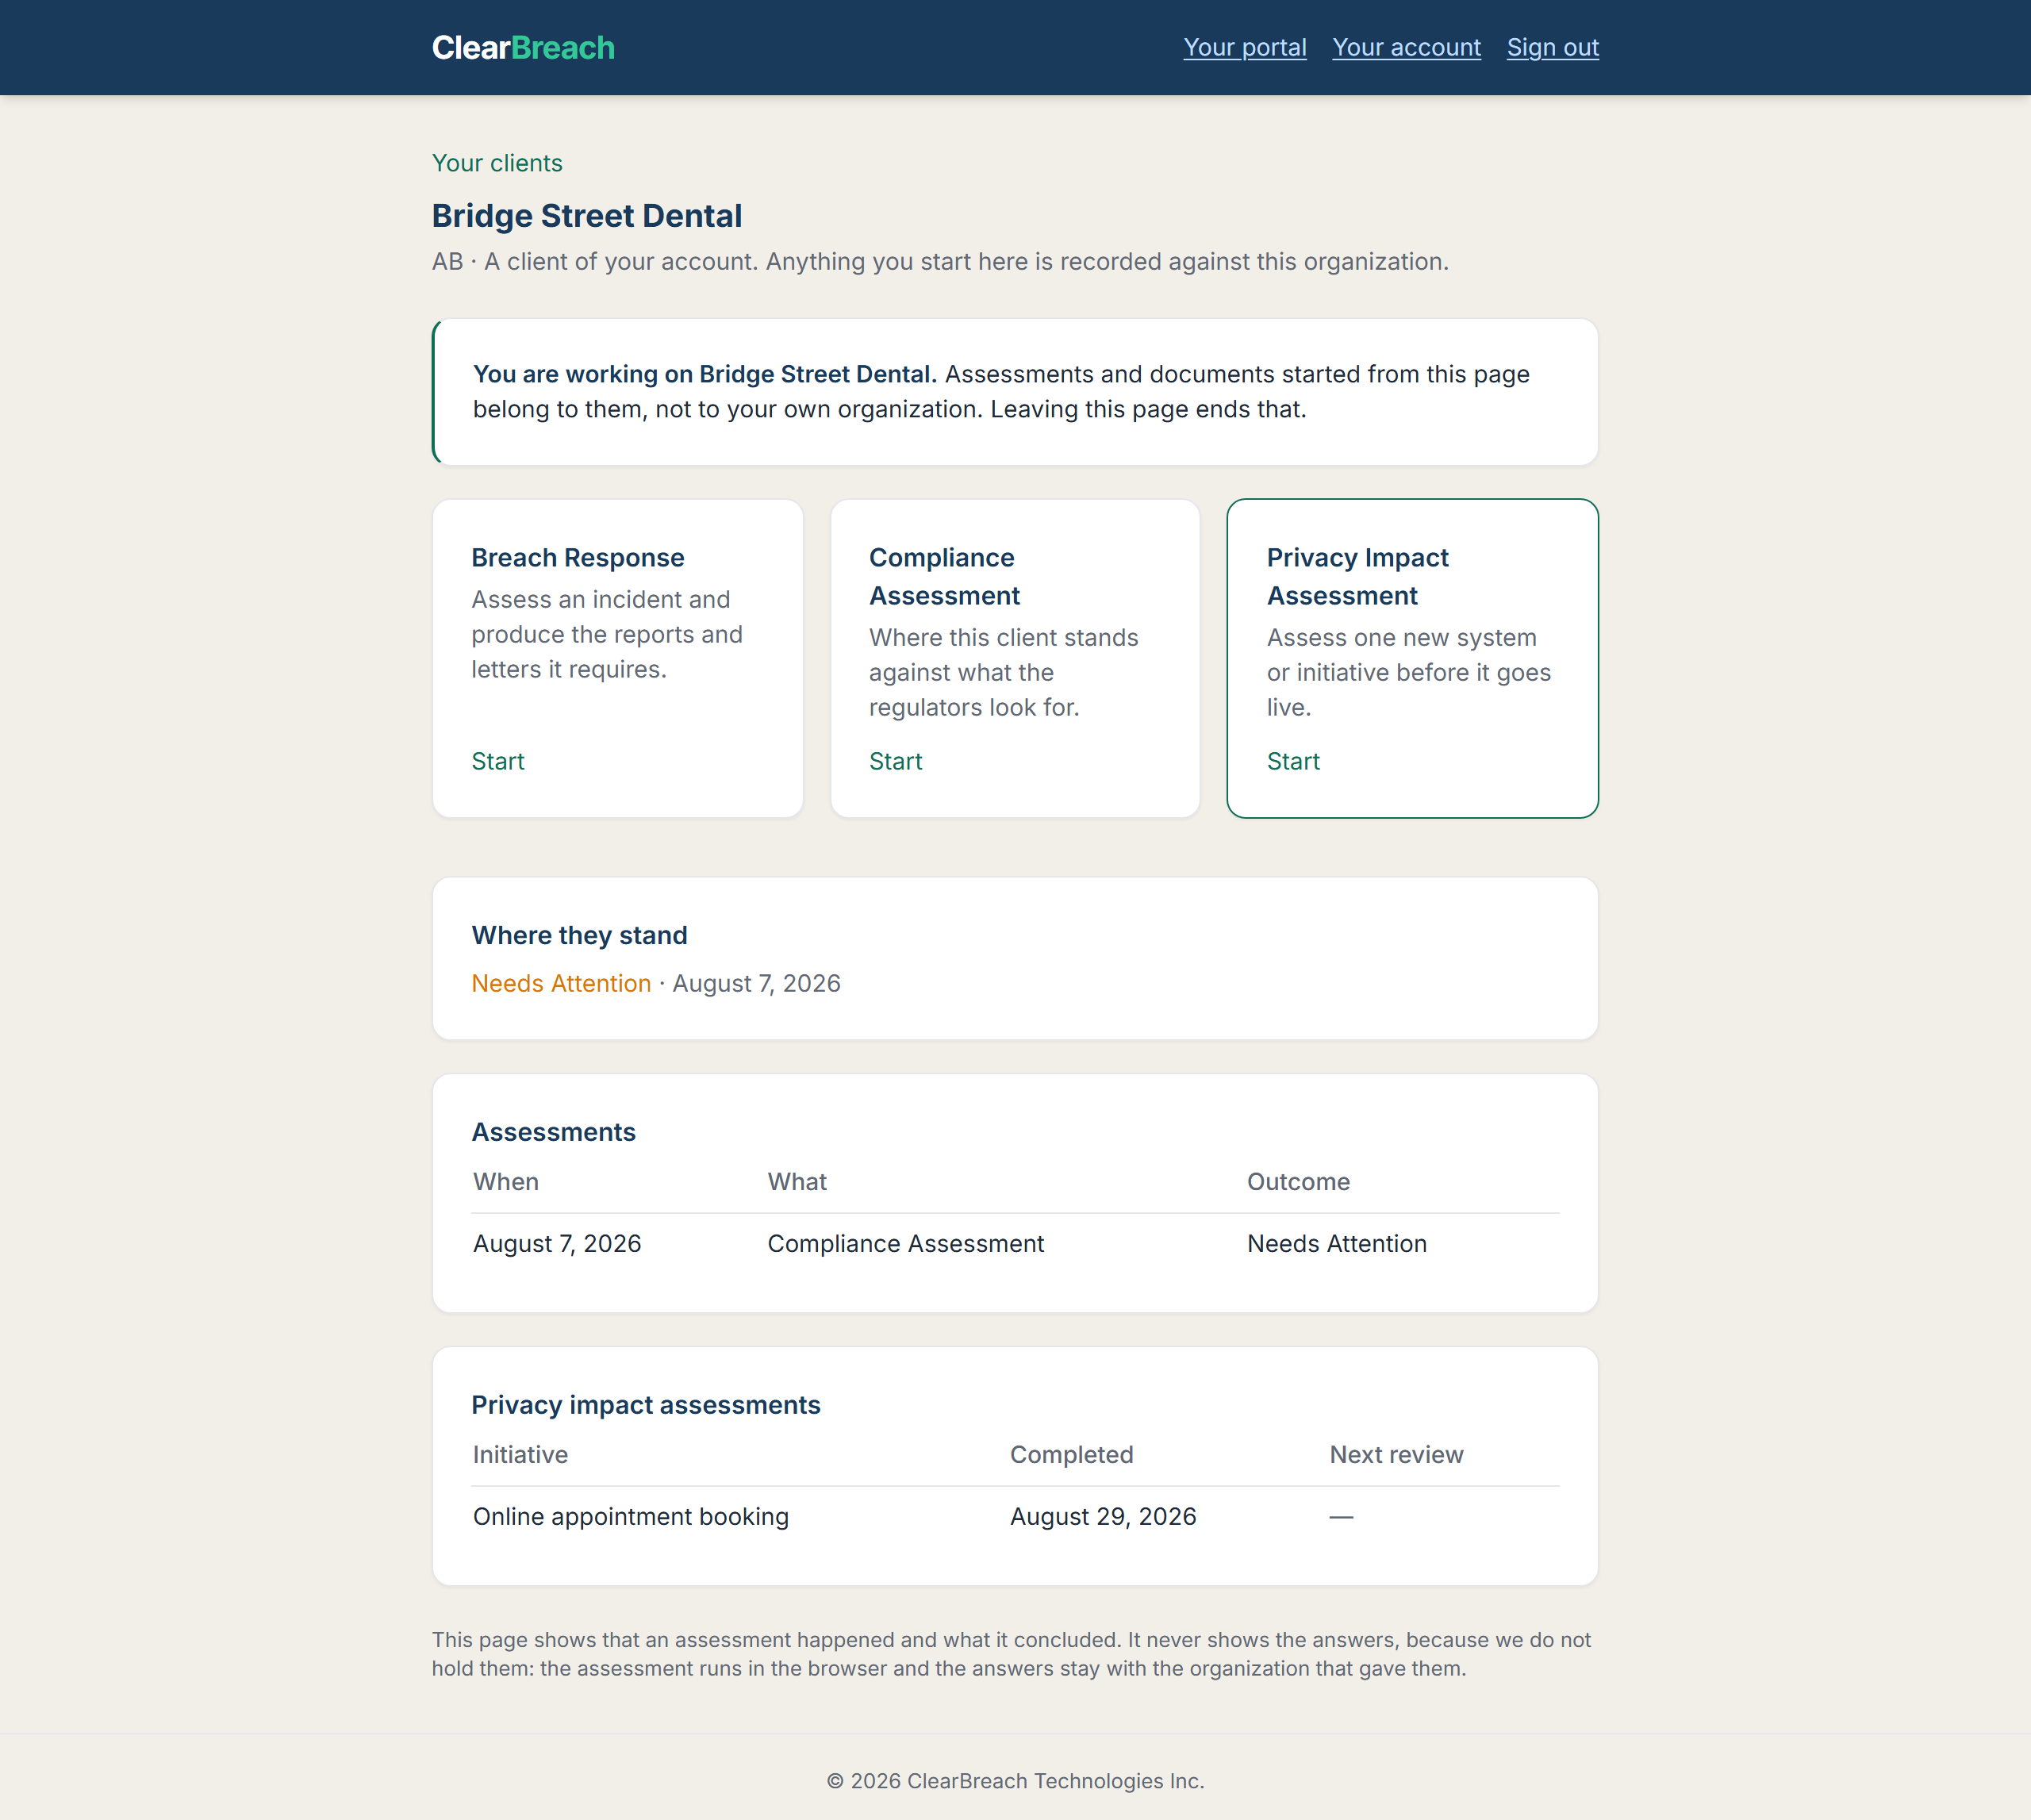
Your clients keep their own records, with your name on them.
This is the half your client sees, and the reason they keep coming back to you.
Their own sign-in
Each client gets its own account and portal, with every assessment, its date and outcome, and where its privacy program stands.
Your name is on it
The client portal names you as their provider. They know who is looking after this, which is the point of you being there.
The records are theirs
What you produce for a client belongs to that client. If the relationship ends, its history does not disappear with your account.
What lands in their hands
Complete assessments for fictional organizations, produced by the same product that runs for your clients. Nothing on them was written for marketing.
Ways to offer it
You decide how it fits your business: inside a managed service you already sell, as an add-on, or as separate work. Four examples of services providers build around it.
Privacy readiness review
- When
- Once a year, or when a client’s customer or insurer starts asking questions.
- You
- Run the compliance assessment with them and go through what is missing.
- Your client gets
- Where they stand, what to fix first, and their policies and procedures written.
- You get
- A yearly service that fits into a review you already hold.
Incident support
- When
- A client calls about a breach.
- You
- Gather the facts with them, run the breach assessment, go through the result, and help with next steps within your own scope.
- Your client gets
- Whether they must report, to whom and by when, with the reports and letters written. The decision and the report stay theirs.
- You get
- A clear answer to give on the worst day of their year.
New-vendor review
- When
- Before a client signs up for new software or a new vendor.
- You
- Run a privacy impact assessment, go through what it found, and handle the technical fixes that fall within your services.
- Your client gets
- What to do before launch, and a completed PIA to keep or file.
- You get
- A reason to be in the room for every new system. PIAs are unlimited on your plan.
Ongoing privacy support
- When
- For clients who want privacy looked after all year.
- You
- The yearly assessment, a PIA for each new system, and help when a customer or insurer asks.
- Your client gets
- A record that builds year on year, ready when anyone asks.
- You get
- Privacy work that comes back every year, not once.
These are examples of your own services, priced as you choose. They are not ClearBreach plans, and ClearBreach does not set or collect what you charge.
Pricing
Per client, a year, from 5 clients. No platform fee. The rate for your band applies to every client, so the whole bill drops at 11 and again at 51. Each client receives the Business plan, which is $799 a year bought directly.
MSP Starter
5–10 clients
MSP Growth
11–50 clients
MSP Scale
51+ clients
Under PIPEDA, Alberta PIPA and BC PIPA, plus applicable taxes:
| Clients | Per client | A year |
|---|---|---|
| 5 | $329 | $1,645 |
| 10 | $329 | $3,290 |
| 11 | $279 | $3,069 |
| 20 | $279 | $5,580 |
| 50 | $279 | $13,950 |
| 51 | $229 | $11,679 |
Plus applicable taxes. Quebec Law 25 is outside our scope. 30-day money-back guarantee, so long as no document has been downloaded for any client.
How a trial works: ask by email and we set up a provider account for you, usually for 30 days. Add your clients and run real assessments for them. If you buy, the same account becomes your paid one, with its clients and records.
Who does what
You help your client work through the assessment. Responsibilities stay clear: your client remains accountable for its information and its decisions.
| ClearBreach | You, the provider | Your client | |
|---|---|---|---|
| Running the assessment | The questions, the assessment and the documents | Answers with or for the client, and is responsible for the answers it enters | Supplies the facts |
| The findings | Each finding with its reason and the section of the law behind it | Explains them within its own competence | Reviews them |
| Deciding what to do | Does not decide | May advise within its service | Decides |
| Technical fixes | Does not carry them out | Under its own agreement with the client | Approves them |
| Legal advice | Does not give it | Only if qualified and engaged to | Gets it where needed |
| Reporting a breach | Writes the reports and letters | May help send them | Remains responsible for reporting and notifying |
As set out in our Terms. It is not legal advice, for you or for your client.
Is it a fit?
A good fit if you
- ✓Look after several small or medium Canadian businesses
- ✓Already handle their security questionnaires, incidents, vendor reviews or vCISO-type work
- ✓Want to offer privacy help without building it yourself
Not the right fit if you need
- –Security frameworks such as SOC 2 or ISO 27001
- –Legal advice, for you or your clients
- –Clients assessed under Quebec Law 25
Written for providers
Practical guidance for the moments that matter in a client relationship. Plain enough to send to a client without editing.
| Week one with a new client | Onboarding a client → the six privacy questions worth asking |
|---|---|
| A client reports a breach | A breach at a client → who notifies whom, and why the duty stays with them |
| A client gets a questionnaire | Answering a client security questionnaire → what the questions are really asking |
| The relationship ends | Offboarding a client → what happens to their compliance records |
Give your clients a more complete service
Start with one client assessment and see how the provider account works.