Breach response and privacy proof
When something goes wrong, know what to do.
When someone asks, have the proof.
After a breach, know whether to report it, to whom and by when, with the letters written. Before a new vendor, know the privacy risks. When a customer or insurer asks, show a dated record of what you have in place.
One plan covers a breach and your annual compliance: $799 a year, plus applicable taxes.Covers PIPEDA, Alberta PIPA and BC PIPA. Quebec is not covered.
Tested against published breach decisions by Canada’s and Alberta’s privacy commissioners: the same answer on every one.
What is happening
ClearBreach shows
You receive
Breach assessment
“We had a privacy incident. Do we have to report it?”
ClearBreach showsWhether you must report, to whom and by when, under each privacy law that applies to you
You receiveThe regulator reports and notice letters, written and ready for you to review and file
What to do first →
Compliance assessment
“A customer sent us a privacy questionnaire.”
ClearBreach showsWhat you have in place, what is missing, and the provision behind each
You receiveAn incident response plan, an internal privacy policy and 5 more documents
What to have ready →
Compliance assessment
“Our insurer is asking about our privacy practices.”
ClearBreach showsWhich privacy questions you can answer yes to today, and which you cannot yet
You receiveA record of what you have in place, to answer from
What insurers ask →
Privacy impact assessment
“We are adding a new vendor or software. Is there a privacy risk?”
ClearBreach showsWhich privacy law applies, and the risks to address before you start
You receiveA completed privacy impact assessment, ready to keep or file
What to check first →
Getting started
“We want our privacy basics in place.”
ClearBreach showsWhich law applies to you, and what to put in place first
You receiveA free starter guide, and the compliance assessment when you are ready
Where to start →
Breach details are assessed in your browser and never sent to us. Canadian hosting. How we handle your information →
Why we exist
Privacy law is written in legal language. A business needs to know what it means for them: what applies, what to decide and what to do.
Getting that right shouldn’t take a privacy team, so we built ClearBreach for businesses without one.
What you get, on three real cases.
Every example below is real output from ClearBreach, not a mock-up. How it works →
Breach response
You found out this morning.
ACME Retail answered 32 questions about one incident affecting 18,400 people. It got an answer under each of the three laws that apply, and 6 documents written, the regulator reports among them.
See a real verdict →Compliance assessment
The insurance renewal asks whether you have a privacy policy.
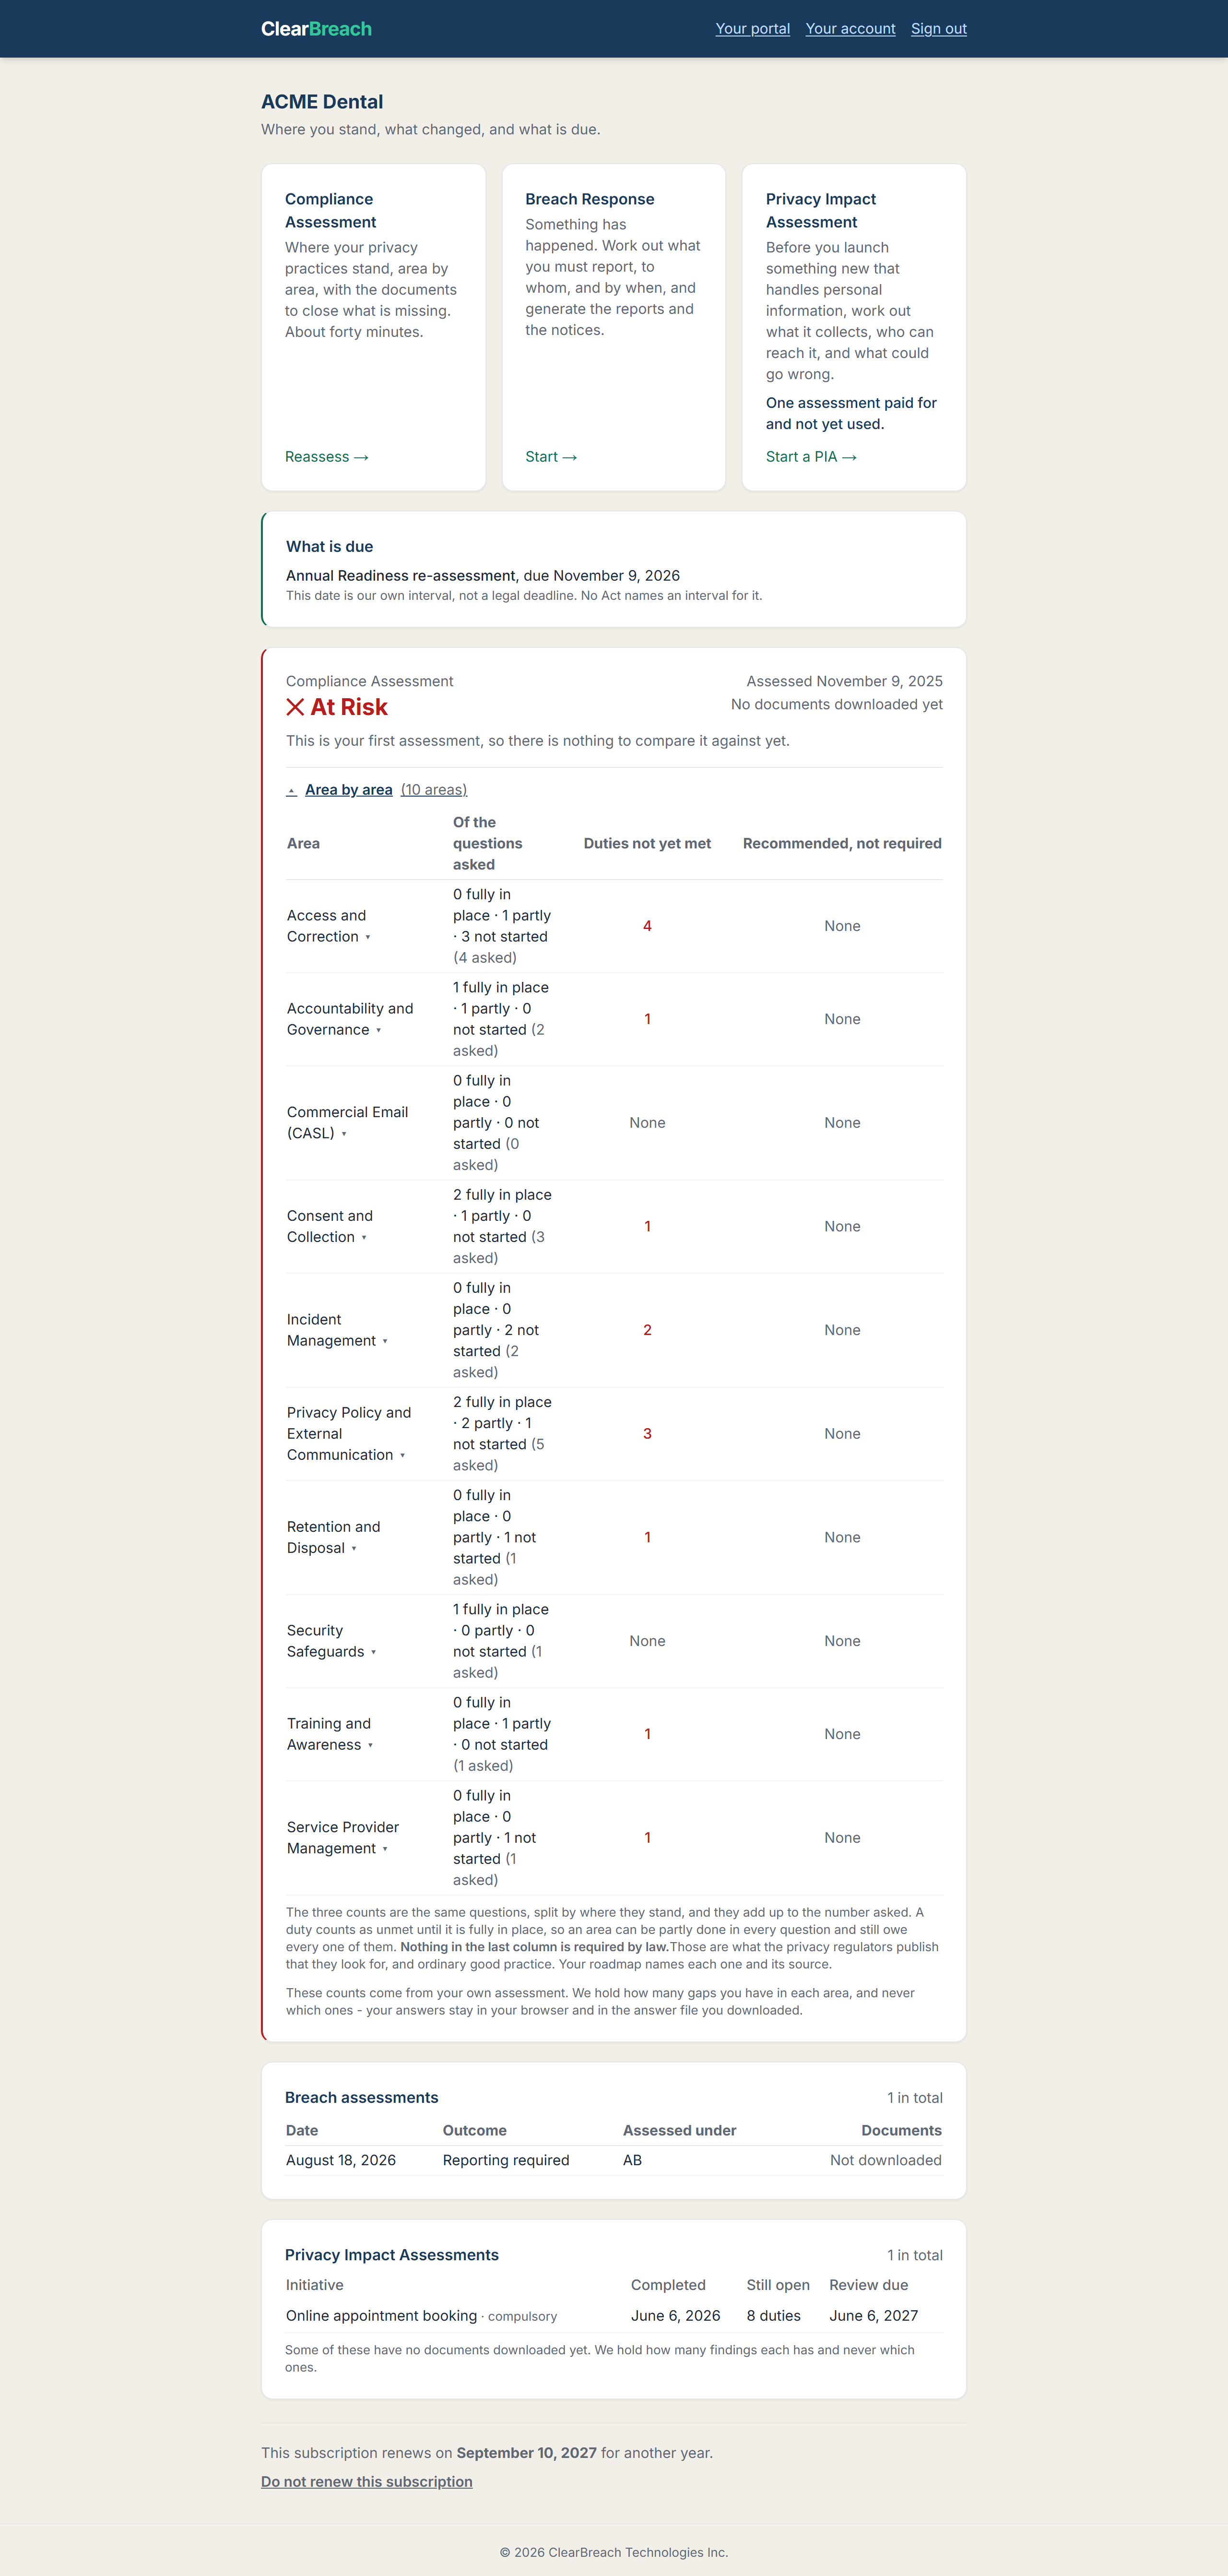
ACME Residential answered 51 questions about how it works. It got an overall status of At Risk, what to fix in each of 10 areas, and 7 documents written from its answers.
See a complete assessment →Privacy impact assessment
You are about to sign up for something.
ACME Residential described its plan for online rental applications. It got the law that covers each of its 2 information flows, 7 duties still to meet before launch, and a completed PIA to keep.
See a completed PIA →Your privacy record becomes more useful over time
When your insurer asks next year, the answer is already there. The record builds as you go, so it is ready before anyone asks.
- Every assessment is kept with its date and outcome, ready when a customer or insurer asks.
- We email you when your annual review is due, and on the review date you set for each vendor.
- We tell you when a law you were assessed against changes.
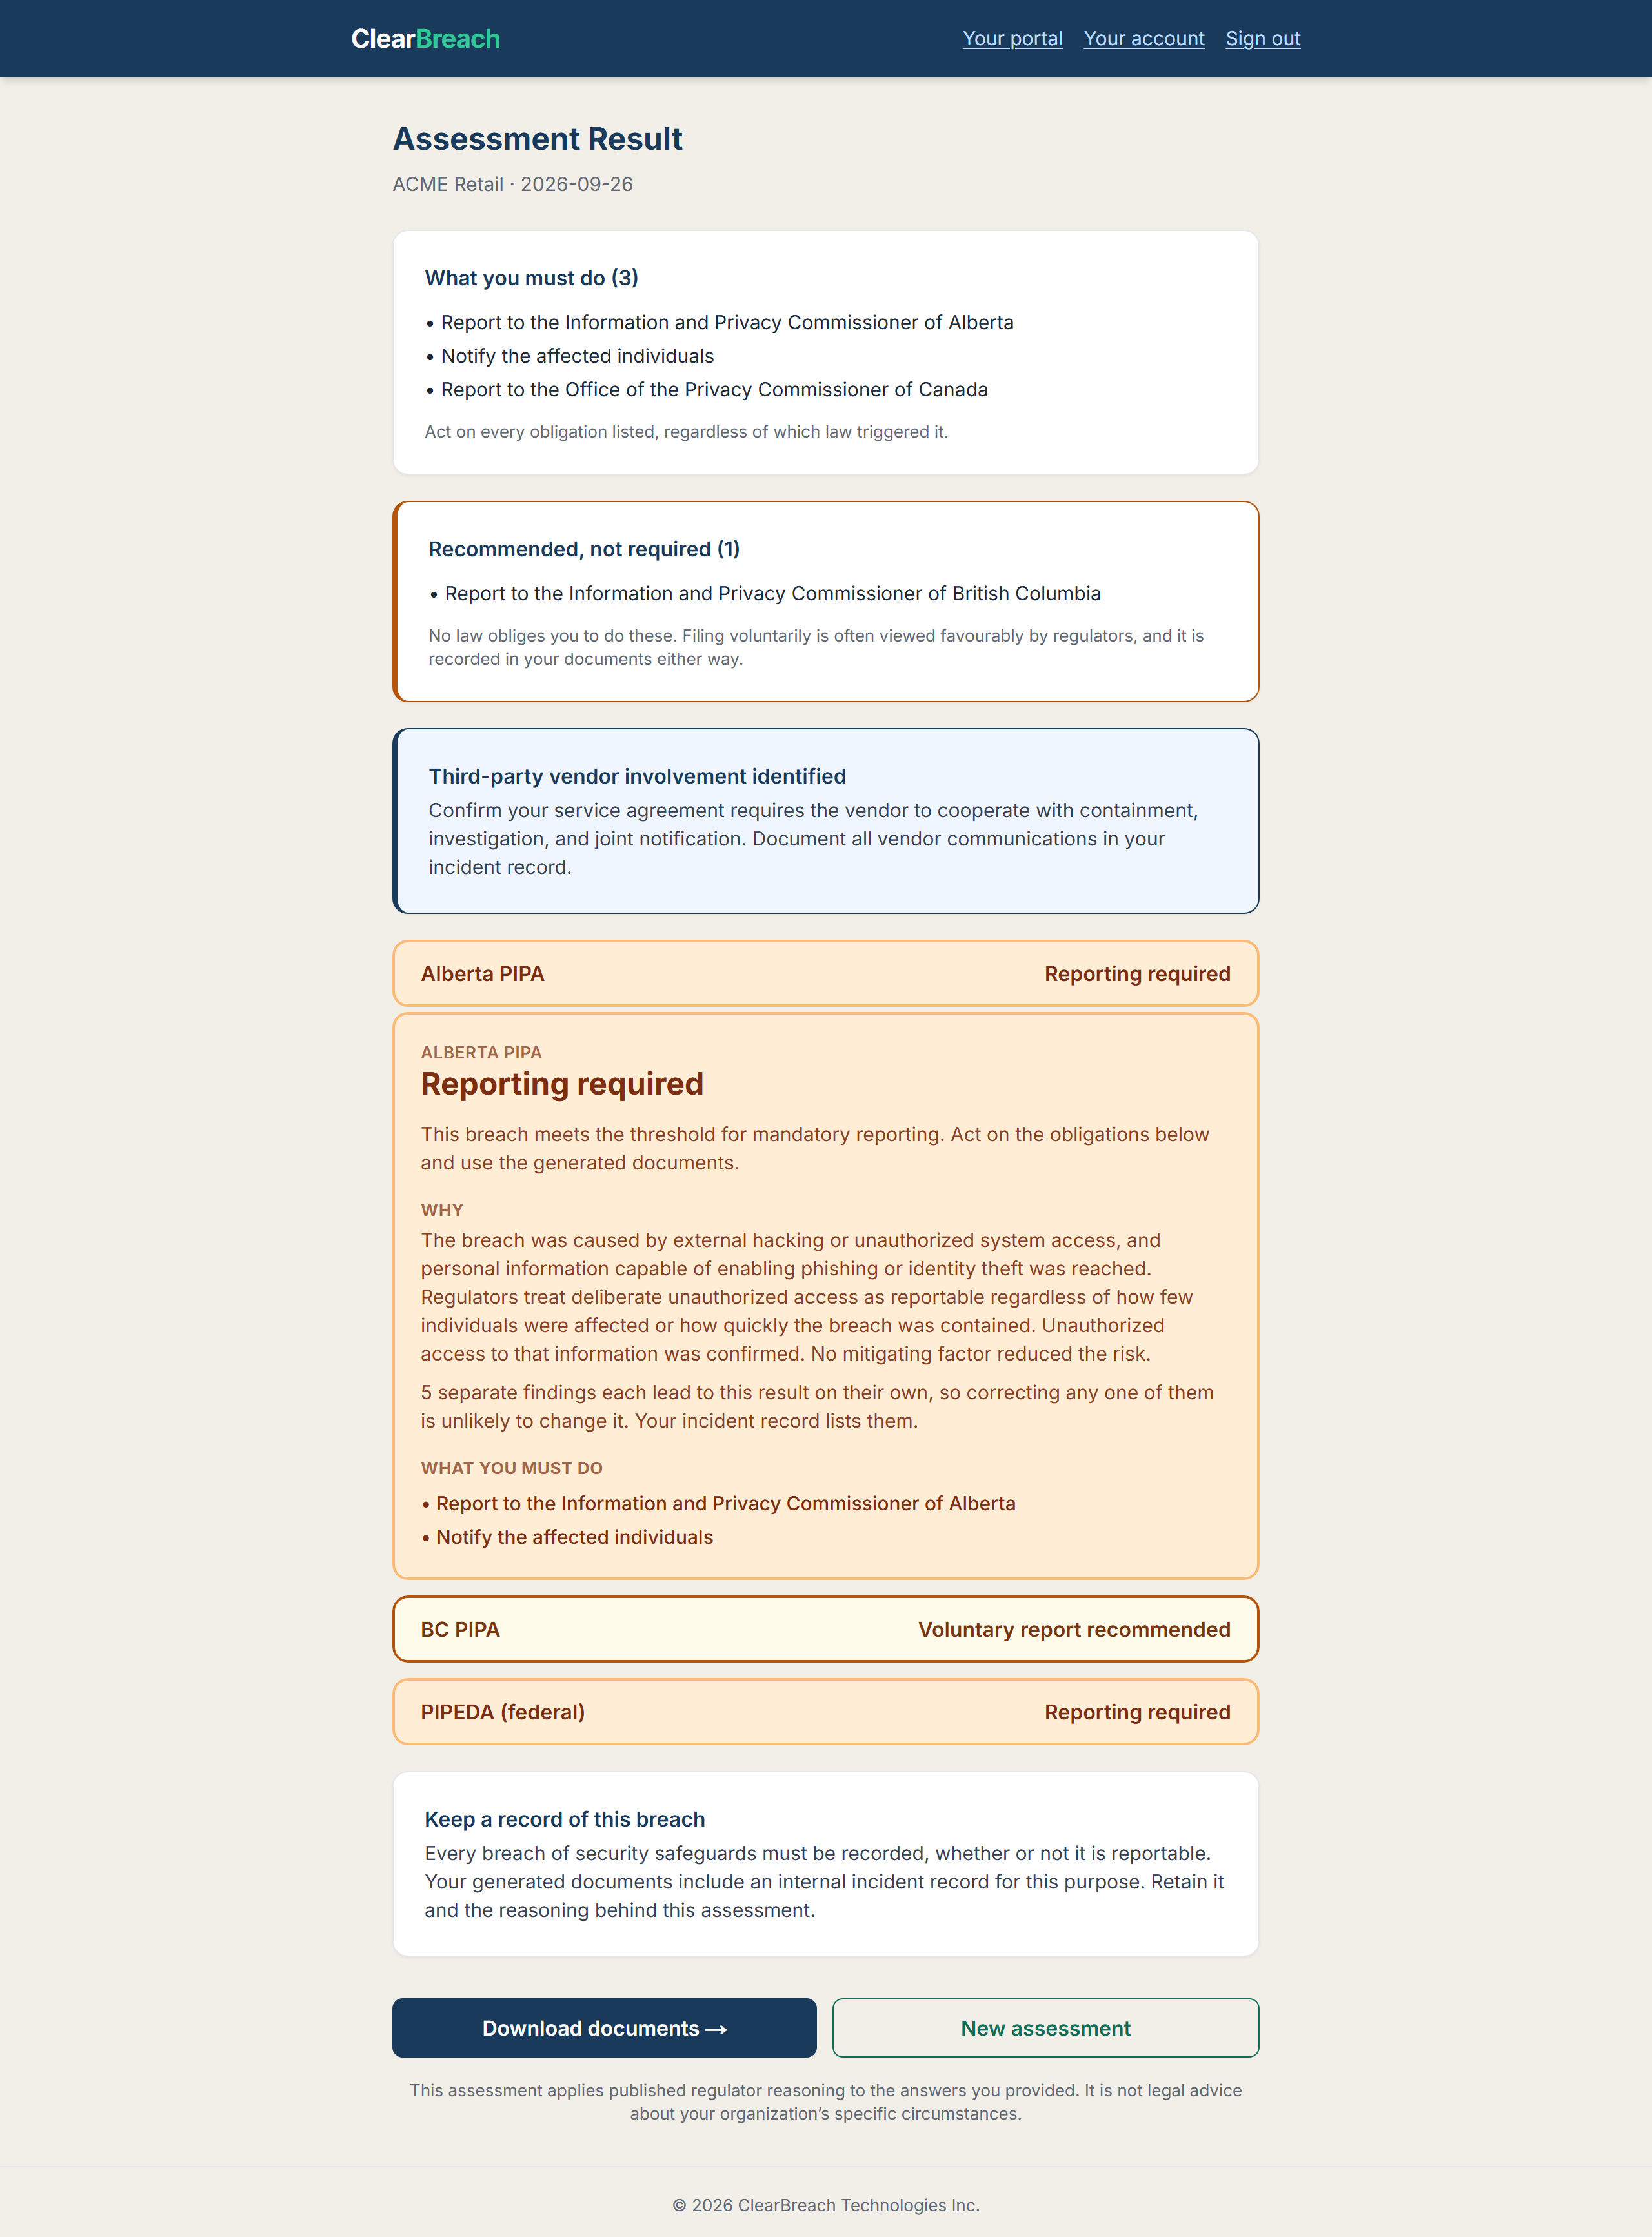
One breach. Three different answers.
ACME Retail had one incident affecting 18,400 people, with customers in Alberta, British Columbia, Ontario and Quebec. The same facts, assessed under every framework that applies to them:
- Alberta PIPA: Reporting required
- BC PIPA: Voluntary report recommended
- PIPEDA: Reporting required
- Documents produced: Assessment Verdict Card, Internal Incident Record, Individual Notification Letter, OPC PIPEDA Breach Report, OIPC Alberta PIPA Report, OIPC BC PIPA Report
Each law gives its own answer, so you do not report where you need not, and do not miss a report where you must.
British Columbia differs because BC PIPA has no mandatory breach-notification trigger, not because the breach is less serious there. Quebec has its own Act, which ClearBreach does not assess. Getting that wrong in either direction is why each Act gets its own answer.
How the breach rules differ in each province, with the section behind each →
Have an answer when a customer asks what you have in place
PIPEDA, Alberta PIPA and BC PIPA expect 12 things of a business, and together they are your privacy program. The compliance assessment shows which you have and which are missing, and writes 5 of them for you from your answers.
Phase 1
What applies to you, and what you hold
You can say what information you hold and which law covers it.
3 steps
Phase 2
What starts a clock
When something goes wrong, or someone asks for their data, you know what to do and how long you have.
3 steps
Phase 3
What you tell people
What you tell customers matches what you actually do.
2 steps
Phase 4
What has to hold every day
It holds up on an ordinary day, not only when someone checks.
4 steps
Who does which part
- Buy and configure2 of 12. Security and email tools you set up: logins, encryption, updates, a working unsubscribe.
- We write it5 of 12. Your inventory, privacy policies, complaint and access-request procedures, and incident plan.
- Only you can decide5 of 12. Which laws apply, who is responsible, what you collect, how long you keep it, and what your vendors sign.
You get where you stand today, what to fix first, and the documents, dated, ready when someone asks.
The 12 are what the law expects of you. The 5 the assessment writes arrive as 7 documents, plus a public privacy policy template where you need one.
Why you can trust it
Built on the text of PIPEDA, Alberta PIPA and BC PIPA and on published regulator guidance. The breach assessment has been tested against published breach decisions by Canada’s and Alberta’s privacy commissioners, and reaches the same answer on every one. It is not legal advice.
Breach details never leave your browser
Your answers about the breach are assessed entirely in your browser. What is recorded is the assessment itself: the overall outcome, how many privacy laws applied, your operating provinces, whether information moves outside them, and the date. Never what happened or to whom.
What the other two assessments keep
The compliance assessment records a score per area and nothing else. A privacy impact assessment does store the name of the initiative and of your privacy officer, because it is a document you file and return to a year later.
Canadian data residency
Production infrastructure is hosted in Canada. Billing is processed by our payment provider in the United States.
ClearBreach Technologies is a Canadian company, founded and led by Yong Du, its privacy officer, after more than a decade in enterprise cybersecurity and IT operations in western Canada. Its assessment framework and every document it produces are built on published OPC and OIPC guidance and enforcement findings.
About ClearBreach, and who is behind it →What it requires of your profession
The law does not have a chapter for dentists and another for mortgage brokers. It has one set of obligations that lands differently depending on what you hold. Pick yours to see what applies to your kind of business.
For IT Service Providers
Add privacy to the services you offer your clients.
When a client has a breach, a new vendor or a customer asking what they have in place, run the assessment for them from one account, each client with their own records. From$329 a client a year, plus applicable taxes, against $799 bought directly.
See how ClearBreach works for MSPs →Ready to get started?
When a breach happens or a customer asks, you do not want to start by working out which law applies and what to prepare. Have the answers and the records in place before you need them.
From a breach found this morning to the proof a customer asks for next month, written from your own answers.
See plans and pricing30-day money-back guarantee, so long as you have not downloaded any documents.
MSP plans available. See pricing.